SECURIN EXPOSURE
Unify every exposure.Fix what attackers will exploit next.
Securin Exposure unifies vulnerability data, threat intelligence, ownership, and remediation workflows so teams can prioritize weaponized risk, route fixes to the right owners, and prove exposure is shrinking over time.
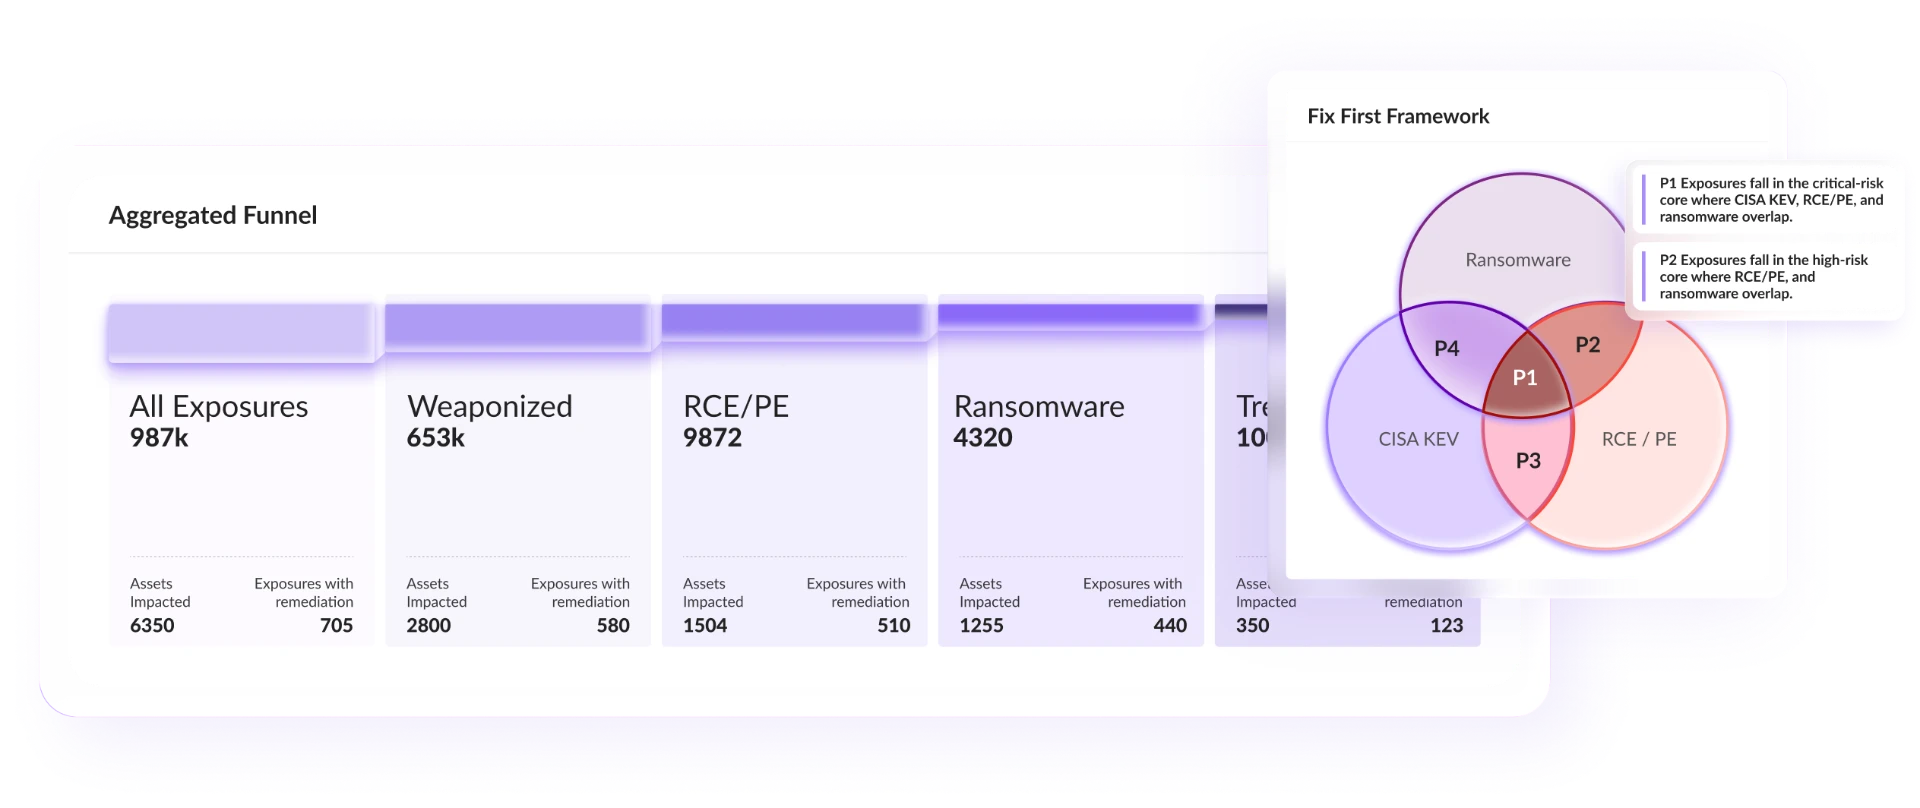
Unified vulnerability management,end to end
Your entire security stack, unified and prioritized into one evidence-backed remediation queue.
Unify every finding into one record
Ingest and deduplicate vulnerability and asset data from 100+ scanners, EDR platforms, cloud tools, and CMDBs into a single golden record, no more reconciling conflicting outputs.
Fix by attacker interest, not CVSS
Predictive, adversary-focused scoring cuts prioritization noise by up to 70%, so remediation effort follows real-world exploitability and business impact.
Validate what's actually exploitable
Confirm exploitability with attack-path context and adversarial validation before remediation effort is spent, theoretical risks leave the queue.
Route fixes to owners automatically
Context-rich tickets land in ServiceNow, Jira, and the workflows engineers already use, with SLAs assigned and tracked, no manual triage.
Get ahead of weaponization
Identify critical vulnerabilities and zero-days, days before CISA KEV listings.
Prove risk is falling
Exposure reduction trends, SLA compliance, and audit-ready program evidence, outcome metrics for the board, not activity counts.
Volume isn't risk, yet most programs rank it that way.
New CVEs were published in 2025, averaging roughly 130 every day
Of vulnerabilities are ever exploited in the wild, representing the narrow slice that actually drives breaches
UNIFIED VISIBILITY
Every tool sees a piece. Nobody sees the whole.
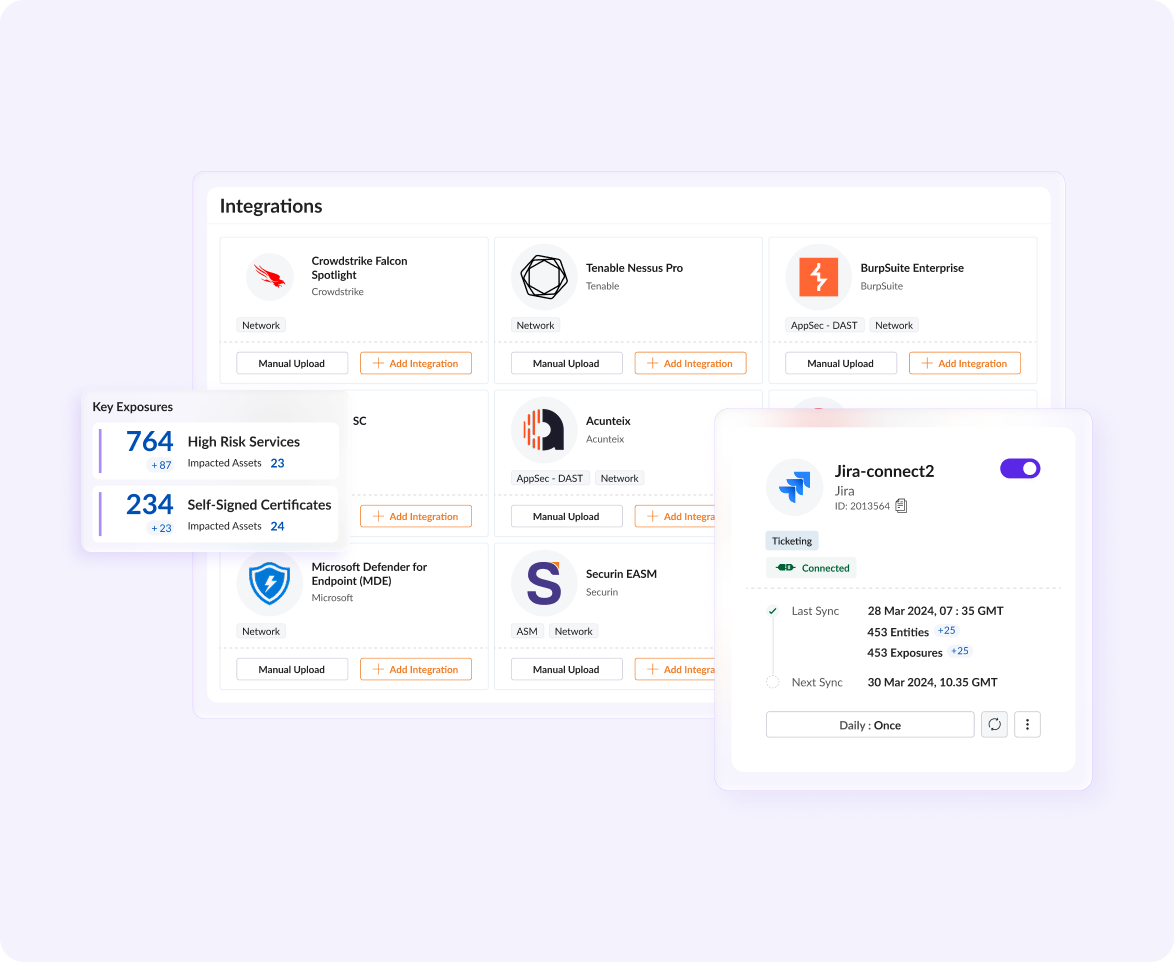
Continuously discover and inventory assets, exposures, applications, and cloud resources across your environment to get a comprehensive view of your attack surface.
- Programmatic ingestion from 100+ connectors - network and application scanners, cloud, EDRs, CMDBs, AI
- Normalization and deduplication into a single trusted "golden record" per asset
- Business context mapping with asset criticality tiers, including Crown Jewel designation for production and high-value infrastructure
RISK-BASED PRIORITIZATION
CVSS is one signal. Building your VM program around it alone isn't a strategy.
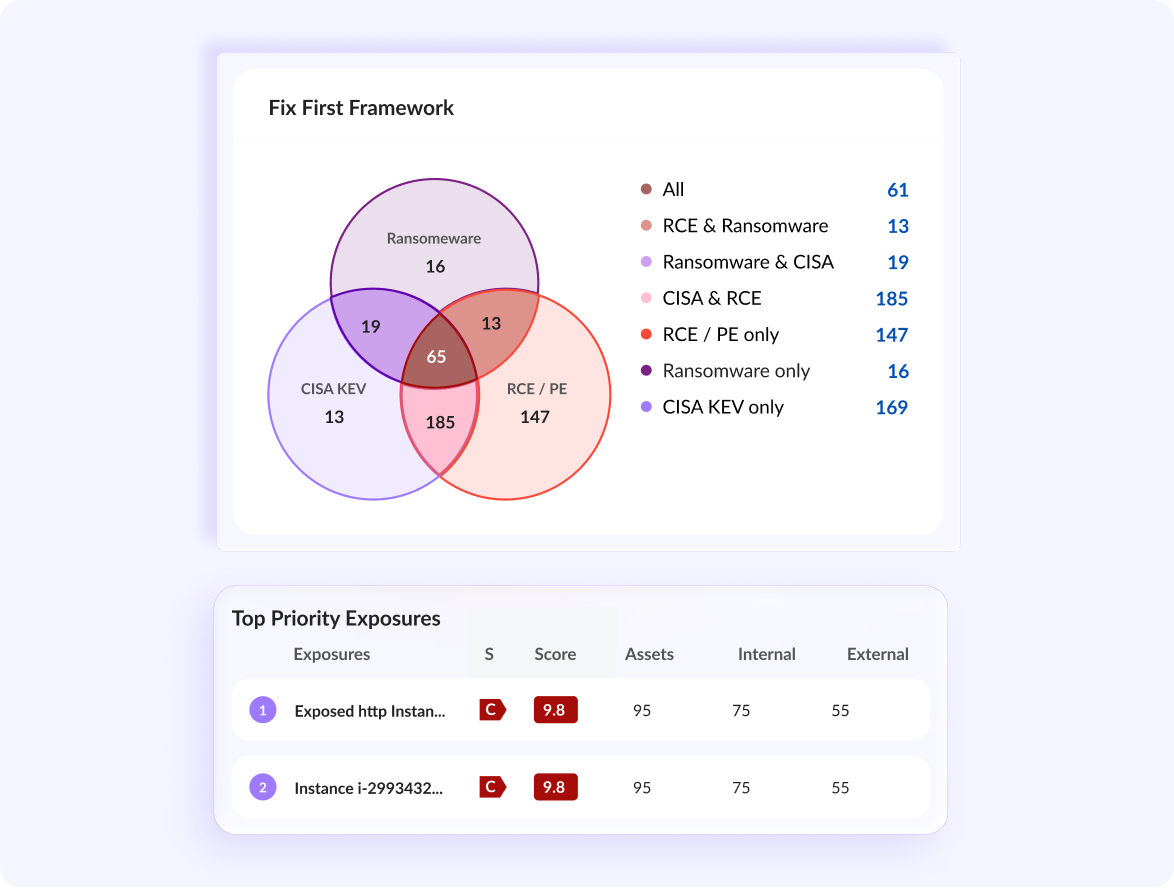
Without weaponization context, a theoretical critical ranks the same as one ransomware groups are actively exploiting. Securin enriches every exposure with in-the-wild status, ransomware and APT correlation, KEV classification, and exploit availability, so the queue reflects what attackers are actually doing, not just what scores say could happen.
- Predictive risk scoring built on adversarial behavior modeling, identifying critical vulnerabilities before widespread exploitation
- Prioritization noise cut by up to 70%, with a reduced exposure list typically within 3–6 months
- Every exposure weighted by business context: crown-jewel status, exposure, and exploitability, not technical severity alone
REMEDIATION ORCHESTRATION
Findings don't fix systems. Owners do.
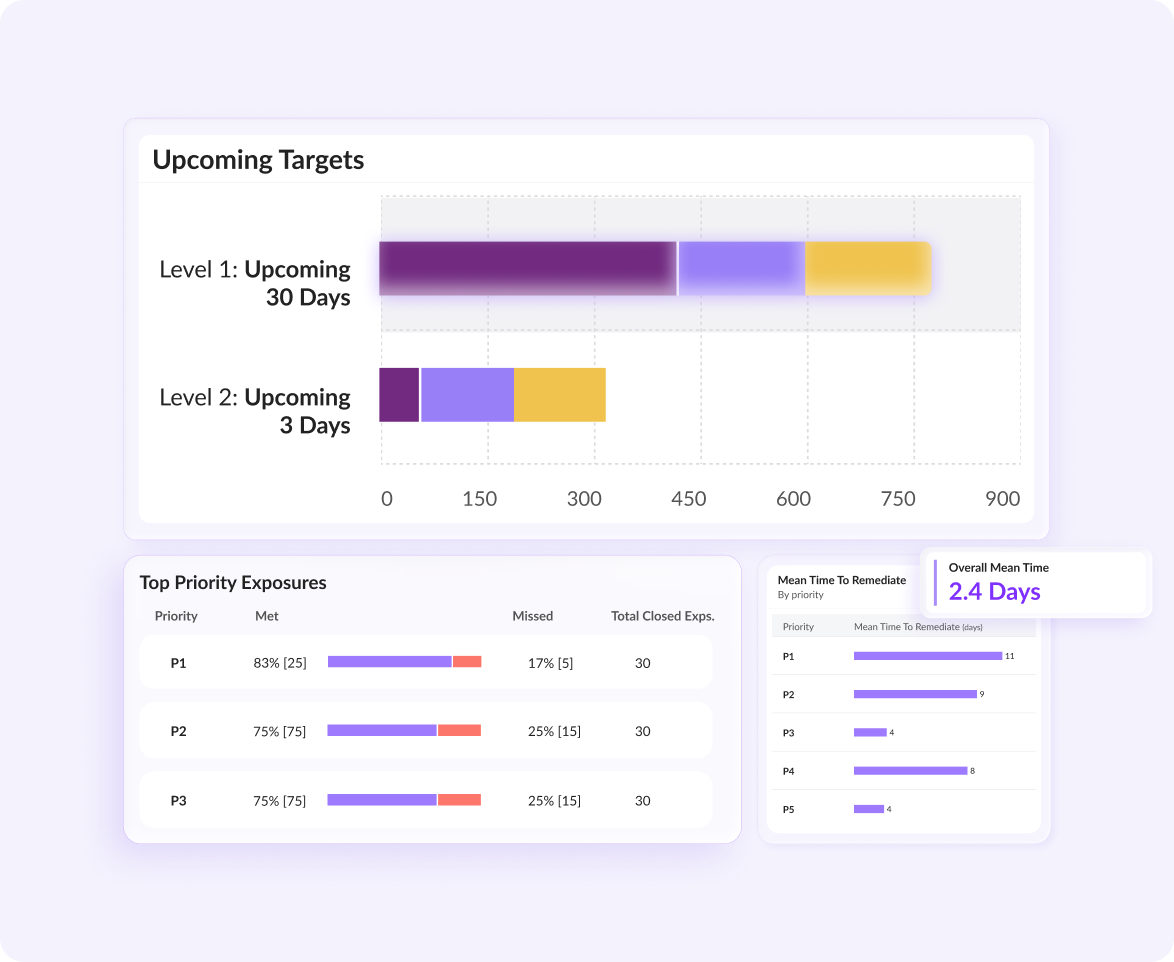
Close the gap between finding and fixing, context-rich tickets routed to the right owner, in the workflows they already use, with SLAs tracked.
- Tickets created automatically in ServiceNow, Jira, and other ITSM platforms with full vulnerability context and exploitability intelligence pre-populated
- Automated SLA assignment, progress tracking, and inbuilt notifications, no analyst intervention required
- Remediation up to 60% faster, because engineers work from the tools and workflows they already use
UNDER THE HOOD
Securin Exposurecapabilities
The continuous program engine, ingestion, prioritization, orchestration, and proof in one place.
Ingestion & Normalization
Programmatically ingests vulnerability and asset data from 100+ connectors, scanners, EDR, cloud security, CMDBs, and normalizes to a deduplicated golden record.
Eliminates conflicting scanner outputs and gives every team one trusted view of the asset.
Business Context Mapping
Assigns asset criticality tiers including Crown Jewel designation for production and high-value infrastructure.
Risk scoring reflects actual business context, not just technical severity.
Predictive Risk Scoring
Prioritizes exposures using adversarial behavior modeling fed by Securin Signals, identifying weaponized vulnerabilities before widespread exploitation.
Surfaces the small set attackers are actually using, not the long tail of CVSS-Critical noise.
Remediation Orchestration
Assigns SLAs, tracks progress, notifies owners, and creates pre-populated ServiceNow / Jira / ITSM tickets with exploitability context.
Engineering teams get actionable, prioritized work items without security having to chase down details.
Unified Dashboard & Reporting
Tracks SLAs, measures exposure reduction over time, and gives executive-ready visibility plus audit-ready proof, with role-based views for technical operators and program stakeholders.
Single source of truth for board, audit, and operational reporting.
OUTCOMES
Outcomes your security leadershipcan stand behind
Confidently answer the questions that matter most: what's our risk exposure, and are we reducing it?
What you get:
Every scanner, agent, and cloud tool deduplicated into a single trusted view.
A queue scoped to active adversarial behavior, reduced within 3–6 months.
Context-rich tickets in the workflows engineers already use, no handoff delays.
Critical vulnerabilities and zero-days flagged up to a week before CISA KEV.
Scoring that reflects business criticality, not just technical severity.
Automated assignment, tracking, and notifications across teams, no spreadsheets.
Exposure trends and audit-ready program evidence, in business terms.
Every finding unified. Every fix justified.
Connect the tools you already have and see your backlog reprioritized by real-world exploitability.